Patient consent and data rules every clinic needs before using an AI scribe
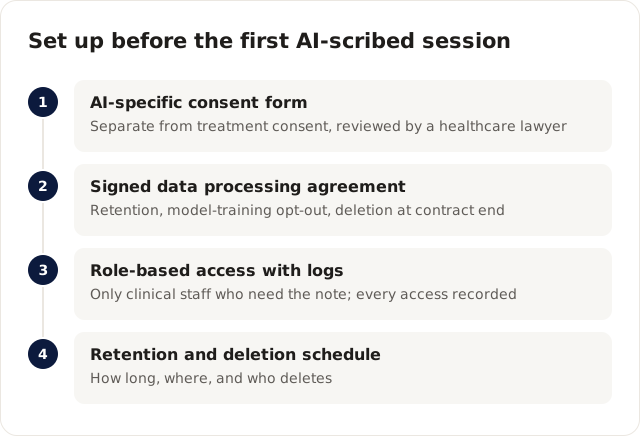
Four things a clinic should have in place before the first AI-scribed consultation: an AI-specific consent form, a vendor data processing agreement, role-based access with logs, and a retention schedule.
On this page
Before a clinic records its first consultation with an AI scribe, four things should be in place: a consent form specific to AI recording, a signed data processing agreement with the vendor, role-based access to transcripts and notes, and a written retention and deletion schedule. The software is the easy part; this setup around it is what protects the clinic when a patient asks questions.
This is for private clinics evaluating an AI scribe. It explains what to prepare and what to ask; it isn't legal advice, so have a healthcare lawyer review your forms and agreements for the places you operate.
Picture the failure case, as an illustration: a clinic starts using a transcription tool without telling patients. Months later a patient complains, and the clinic has no signed consent, no agreement with the vendor and no retention policy. The tool may be fine. The setup isn't.
If you're evaluating an AI Medical Scribe System, plan this compliance work before any recording happens.
What patients need to know before a session begins
Consent for an AI scribe is different from treatment consent. The patient agrees to have the consultation recorded, processed by software, and possibly stored outside the clinic's own servers.
The form should name the tool, explain what it does, state where the data goes, and offer a real opt-out. Real means that if the patient declines, the consultation goes ahead without the scribe and nobody makes them feel awkward for asking.
Written consent, dated and kept in the patient record, is the safer default even where verbal consent might be allowed. Rules differ by state and country (in India, for example, the Digital Personal Data Protection Act, 2023 applies to personal data), so check each location you operate in.
The data processing agreement many clinics skip
When a vendor processes patient audio or transcripts, your clinic is generally the controller of that data and the vendor the processor. That relationship needs a signed data processing agreement (DPA) before you go live.
The DPA should say what data the vendor can access, how long they keep it, whether they use it to train models, and what happens to it if you end the contract. If a vendor won't sign a DPA or can't produce one quickly, treat that as an answer.
HHS guidance on HIPAA Business Associate Agreements sets out what a US vendor handling protected health information must agree to. Even if your clinic falls under a different law, it is a useful checklist for what a vendor agreement should cover.
Where clinics get storage and access wrong
Transcripts and AI-drafted notes are clinical records, as sensitive as lab results or prescription history. A shared Google Drive folder, or access for all staff by default, creates risk nobody needs.
Access should follow the rules for the rest of the medical record: by role, logged, and reviewed now and then. The doctor who ran the consultation needs access. The front desk generally doesn't.
Keep audit logs. If there's a complaint or a patient asks for their data, you need to show who opened what and when. Either the scribe system or your clinic's own software should record this.
Four things to set up before your first AI-scribed session
- A consent form for AI recording: separate from treatment consent, reviewed by a healthcare lawyer, signed before the first session.
- A signed DPA with your vendor: retention periods, model-training opt-out, deletion when the contract ends.
- Role-based access to transcripts: only clinical staff who need the note can see it, and every access is logged.
- A written retention and deletion schedule: how long transcripts are kept, where, and who deletes them when the period ends.
With a clear internal policy and a vendor who already has these documents, this is days of work, not months.
What happens when a patient asks for their data
Most modern privacy laws give patients the right to request a copy of their data, and many give a right to ask for deletion, subject to medical record-keeping rules. If transcripts sit in a vendor's cloud, you need to know how to retrieve or delete them on request.
Ask the vendor directly: "If a patient asks me to delete all records of their consultations, can you do that, and how long does it take?" A vague answer is a gap in your compliance.
Your clinic's internal policy should name one person who handles these requests. It needn't be a full-time role, but someone has to own it.
Cloudgramam sets up AI scribe systems with consent and data handling mapped to the clinic's privacy requirements in the first week, including local or on-device processing where that is needed. If your clinic is ready to move on this, get in touch.